
Compliance Services · HIPAA
HIPAA compliance, managed year-round, not just at audit time.
For medical practices, specialty groups, and the businesses that handle their patient data. ITSco runs the technology side of HIPAA as an ongoing service, so you stay audit-ready every month instead of scrambling before an audit.
Why It Matters
HIPAA is not a one-time project. Your risk changes every month.
Every new hire, laptop, cloud app, and vendor changes how patient data moves through your practice, and the HIPAA Security Rule expects your safeguards to keep pace. When the HHS Office for Civil Rights investigates a breach, one of the first documents it asks for is your security risk analysis, and a missing or outdated one is among the failures it cites most often.
ITSco handles the technology side of HIPAA: the risk assessment, the safeguards it calls for, the documentation that proves them, and the monitoring that keeps them in place. Your attorney and compliance officer decide what HIPAA requires of your organization. We make sure your systems meet it, and we build that work into a predictable monthly cost.
The rules are also changing. In January 2025, HHS proposed a major update to the Security Rule with stricter requirements for encryption, multi-factor authentication, asset inventories, and annual compliance audits. It is not final yet, and regulators now target 2027, but practices that close those gaps now will not face a rushed project later.
1996
Protecting Triangle businesses since
0
Clients with a serious security breach
60%
Of clients with ITSco 5+ years
What's Included
Every HIPAA safeguard, managed and documented.
HIPAA Security Risk Assessment
A documented, dated analysis of every system that touches patient data, with a prioritized plan to close the gaps. Refreshed every year and after any major change.
Policies & Documentation
Written safeguards, procedures, and evidence kept current, so you can show an auditor what you do instead of describing it.
Technical Safeguards
Multi-factor authentication, encryption, endpoint protection, and access controls on every device and account that handles protected health information.
24/7 Monitoring & Response
Around-the-clock threat detection and a documented incident response process, so a suspicious login is handled before it becomes a reportable breach.
Backup & Disaster Recovery
Encrypted, tested backups and a recovery plan that keep patient records available after ransomware or an outage, as HIPAA’s contingency requirements expect.
HIPAA-Ready Microsoft 365
Email encryption, data loss prevention, retention, and access settings configured for patient data, so your email and files hold up to a HIPAA review.
Vendor & BAA Management
An inventory of every vendor that touches patient data and the Business Associate Agreements that should cover them, from your EHR to your backup service.
Training & Audit Readiness
Staff security training with completion records, plus an evidence package ready for an auditor, insurer, or acquirer whenever they ask.
Trusted by businesses across NC, SC & VA


Client Story · EmergeOrtho
HIPAA-aligned from the first design decision.
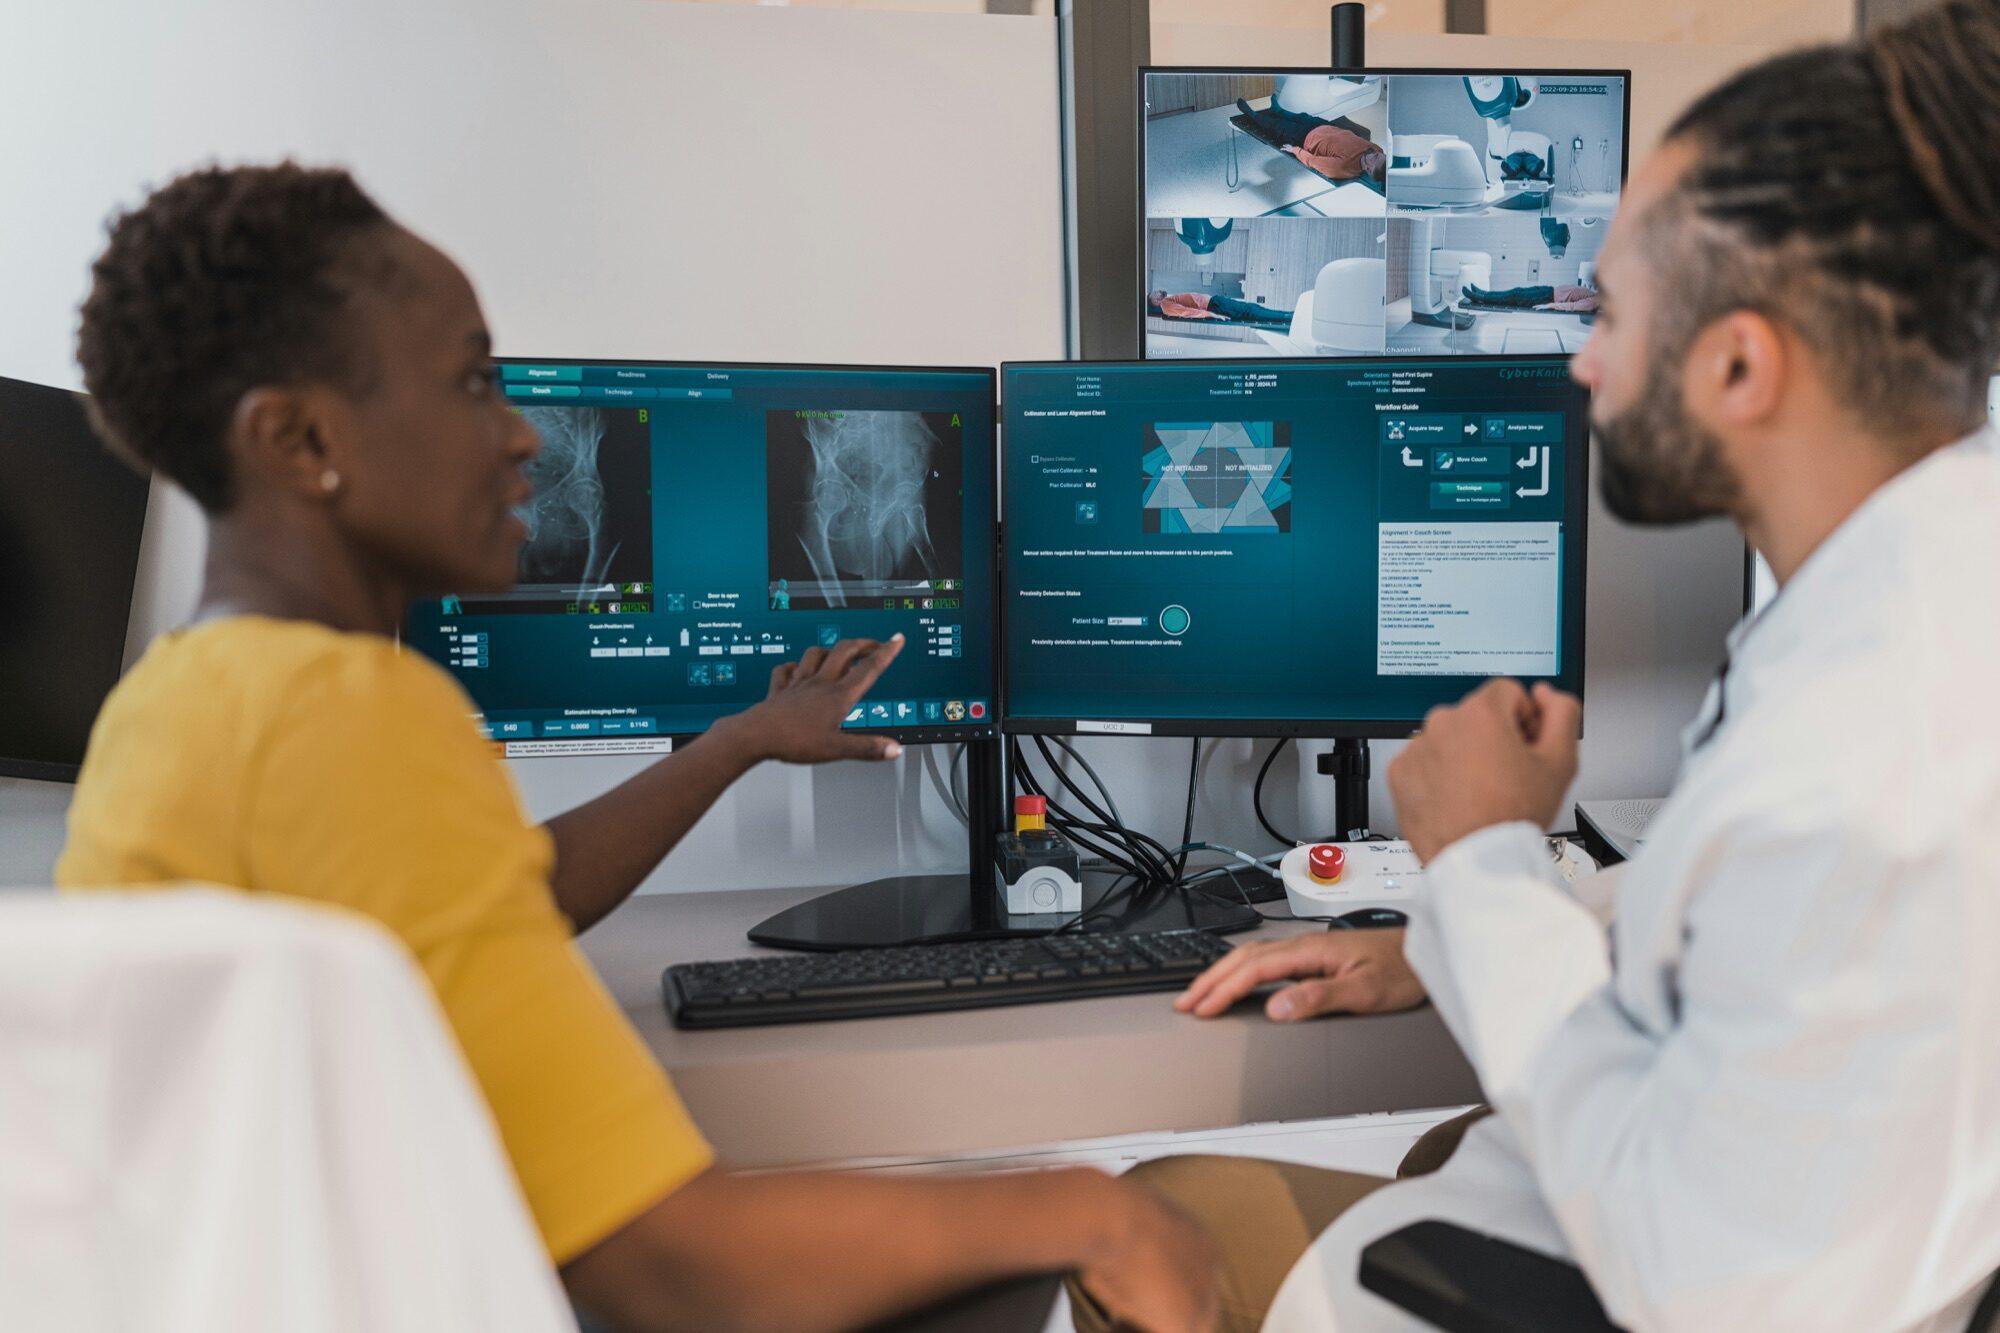
EmergeOrtho, a multi-location orthopedic practice in North Carolina, wanted to operate its mobile MRI trucks remotely so one technologist could run scans across several sites. ITSco designed a network that holds up on the highway, encrypted patient data in transit, tied access to Active Directory, and built the whole system into EmergeOrtho’s HIPAA-compliant infrastructure.
The result was more patient access and lower cost, with compliance designed in from the start. Read the full EmergeOrtho case study.
- 40 extra hours of MRI scanning per week, per truck
- 30 to 40% lower labor costs
- A 4 to 5 month project payback
- Patient data encrypted in transit, with access tied to Active Directory
Ready when you are
One conversation. A clear picture of where your IT stands.
Book a Free ConsultationIn Their Words
What our clients are saying.
“ITSco has provided our technical support for the past 22 years, and, without a doubt, it has been the best vendor relationship that I have had in my professional career. They are reliable, honest, and have been a true partner through all our growth.”
“With ITSco, we get great technical advice from people who actually care about the success of our business. ITSco is responsive to our needs no matter what level of support is requested.”
“We have had a working relationship with ITSco for over ten years. ITSco is always there for us when we need them, and they have helped build up our IT infrastructure with robust resources that fit our security and everyday needs.”
Explore more healthcare and compliance services
FAQ
HIPAA compliance, answered.
What do HIPAA compliance services include?
HIPAA compliance services cover the technology side of the Security Rule: a documented security risk assessment, the safeguards it calls for (encryption, multi-factor authentication, monitoring, and backups), written policies and evidence, staff training, vendor Business Associate Agreements, and an annual reassessment. ITSco runs all of it as an ongoing service, not a one-time project.
What is a HIPAA security risk assessment, and how often do we need one?
It is a documented review of every system that stores or moves patient data, the threats to each, and what you are doing about them. HIPAA requires one, and investigators ask for it early. Update it at least once a year and after any major change, such as a new EHR, office, or cloud system.
Does our IT provider need to sign a Business Associate Agreement?
Yes, if they can access protected health information, and nearly every IT provider can. A Business Associate Agreement makes the provider legally responsible for safeguarding that data. ITSco signs BAAs with healthcare clients and helps you inventory the other vendors that need one, from your EHR to your email and backup services.
Is Microsoft 365 HIPAA compliant?
Microsoft 365 can support HIPAA compliance, but not out of the box. Microsoft will sign a Business Associate Agreement, and your tenant still needs the right settings: email encryption, multi-factor authentication, data loss prevention, retention, and access controls. Default setups are a common gap. ITSco configures and monitors these settings for healthcare clients.
What is changing in the HIPAA Security Rule?
HHS proposed a major Security Rule update in January 2025, adding stricter requirements for encryption, multi-factor authentication, asset inventories, and annual compliance audits. It is not final; regulators now target 2027, and the current rule stays in force until then. Practices that close those gaps now avoid a rushed project later.
Who has to comply with HIPAA?
Covered entities, meaning healthcare providers, health plans, and clearinghouses, plus their business associates: any vendor that handles patient data on their behalf, such as billing companies, IT providers, and law firms. Business associates are directly liable for Security Rule violations, so HIPAA reaches well beyond the practice itself.
How long does it take to become HIPAA compliant?
Most small and mid-size practices can close their highest-risk gaps in about 90 days: the risk assessment first, then the critical safeguards, then documentation and training. Staying compliant is ongoing after that. Our 90-day HIPAA roadmap walks through the sequence step by step.
Can ITSco work alongside our existing IT person or team?
Yes. Many practices keep an internal IT person for day-to-day support and bring in ITSco for the compliance work: the risk assessment, security monitoring, documentation, and audit preparation. We share the evidence and the remediation plan, so your team always knows what is covered and who owns each task.
How are HIPAA compliance services priced?
As a predictable monthly fee built into your IT services, not a surprise project before an audit. The price depends on your users and locations, the systems that hold patient data, and the safeguards already in place. Our IT Investment Calculator estimates your monthly IT cost in minutes, and a free consultation turns that into a number for your practice.
Do you work with healthcare organizations outside Raleigh and Durham?
Yes. ITSco is based in Durham with an office in Raleigh, and we work with healthcare organizations well beyond the Triangle. Most compliance work, from monitoring to documentation, happens remotely, so distance is rarely a barrier. When your organization needs on-site work, we build it into the scope based on your locations and needs.
Free 30-Minute Consultation
Book your free 30-minute consultation with ITSco
Connect with trusted IT experts to scope challenges, identify risks, and drive better business outcomes.